Yacht Cybersecurity in 2026: A Practical Guide for Captains and Owners
Yacht cybersecurity is no longer a niche concern reserved for naval architects or IT departments. In 2026, every yacht — from a 24-metre charter vessel to a 100-metre superyacht — runs on a complex mix of operational systems, crew devices, owner devices, guest networks, and shoreside integrations. Each of those systems is a door. Each door, if left ajar, is an attack surface. And the threats targeting the yachting sector have never been more sophisticated, more automated, or more economically motivated.
This guide is written for captains, owners, fleet managers and IT consultants who want to understand the cybersecurity landscape in yachting today, the regulations that apply, and the practical steps that meaningfully reduce risk — without paralysing day-to-day operations.
"In 2026, the most significant cybersecurity risk will come from inside the perimeter — insider risk, whether malicious, compromised, or accidental, is one of the hardest challenges to detect and manage as organisations become more digitally integrated."— Maritime cyber risk report, 2026
The Threat Landscape in 2026
The threats facing yachts in 2026 fall into a few well-defined categories. Phishing remains the single most common entry point: a crew member receives an email that appears to come from a port agent, a supplier, or a bank, and clicks a link that drops malware or credential-stealing software onto a connected device. Ransomware, which encrypts files and demands payment in cryptocurrency, has spread from corporate networks to maritime ones and now affects vessel-management software, charter booking platforms, and even bridge electronics.
Beyond email-borne attacks, three vessel-specific threats deserve particular attention. GPS spoofing, where a fake GPS signal overrides the real one to mislead navigation, has become alarmingly accessible thanks to inexpensive hardware. AIS manipulation can hide a yacht's position, fake another vessel's identity, or trigger false collision alarms. Wi-Fi pineapple attacks — where a malicious access point impersonates a marina or onboard network — silently capture credentials and unencrypted traffic from crew and guests.
Recent threat-intelligence reports indicate that up to 60% of newly disclosed software vulnerabilities relevant to ships and onshore operations are weaponised within 48 hours, as attackers increasingly use AI to accelerate exploit development. The arms race is no longer a metaphor: it is the operational reality of maritime IT.
The Regulatory Backbone: IMO MSC.428(98)
Since 2021, the International Maritime Organization's resolution MSC.428(98) has required cyber risk management to be addressed in Safety Management Systems under the ISM Code. While initially focused on commercial shipping, port-state inspections increasingly look for cyber-risk evidence on yachts above 500 GT, particularly those operating commercially under charter.
Practically, this means a yacht's SMS must include: a documented risk assessment, written procedures for incident response, evidence of crew training, and a regular review cycle. Class societies (Lloyd's Register, DNV, Bureau Veritas, RINA) all publish cyber-readiness notations, and several insurance underwriters now require a baseline assessment as a precondition for cyber coverage.
Network Architecture: The Foundation
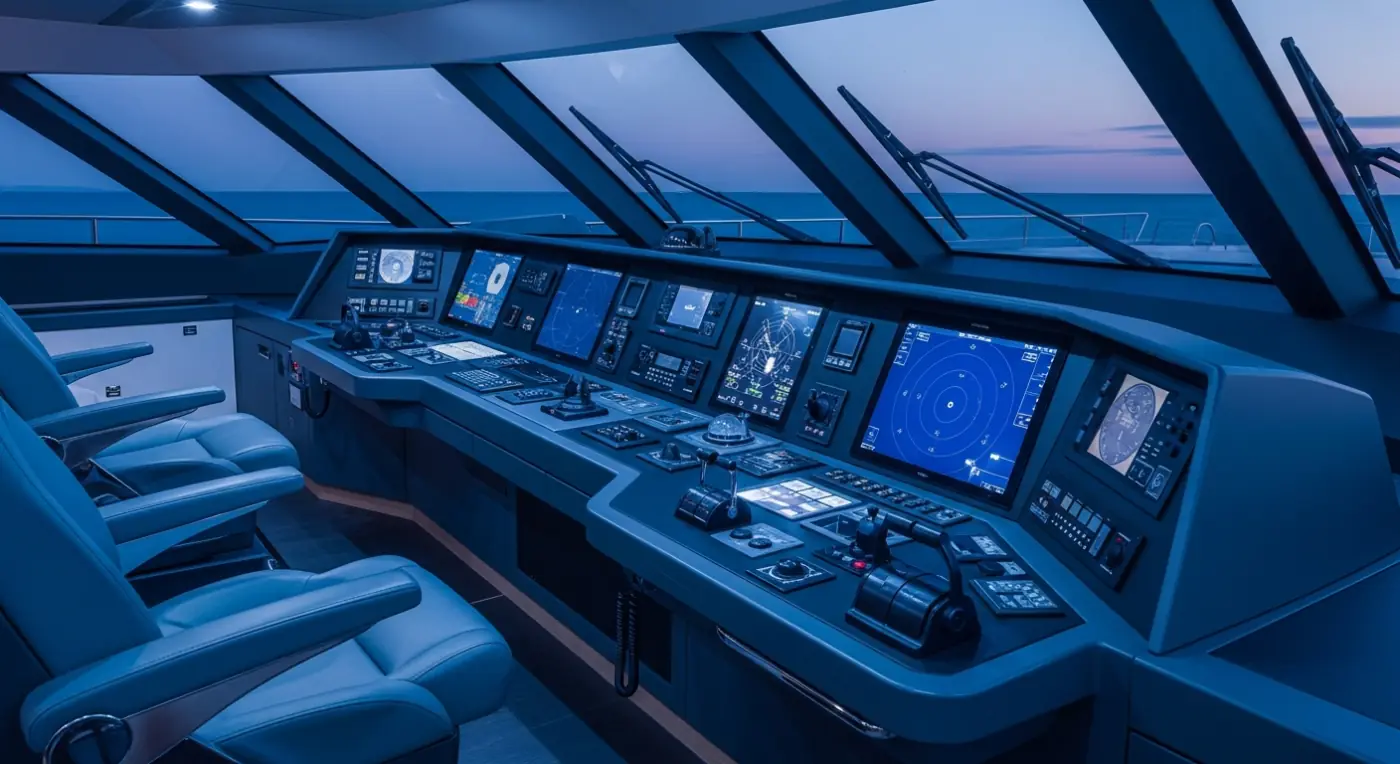
The most effective cybersecurity intervention you can make on a yacht is also the least glamorous: network segmentation. Operational technology (OT) — the navigation, propulsion, machinery and safety systems — must be physically and logically separated from information technology (IT) — crew laptops, guest Wi-Fi, owner devices, entertainment systems.
A well-architected yacht network has at least four distinct VLANs:
- OT network: ECDIS, autopilot, AMS, radars, AIS. Strictly read-only from any other network. No internet access.
- Crew network: Operational devices used for daily work. Outbound internet through a managed firewall, no inbound exposure.
- Guest network: Pleasure Wi-Fi for owners and guests. Fully isolated from crew and OT, with bandwidth limits and content filtering.
- Management network: Used by the IT team for remote support. Separate authentication, audit logged.
Add to this a properly configured firewall, automatic security updates on all crew devices, and a VPN for any remote work, and you've already eliminated the great majority of attack vectors. The CISA cybersecurity advisories publish regular guidance for OT environments that translates directly into yacht network design.
Identity, Access and the Principle of Least Privilege
Almost every cyber incident in yachting in the last three years involved a stolen, shared, or weak credential. The remediation is conceptually simple: enforce strong, unique passwords through a password manager; require multi-factor authentication on every account that supports it; and grant access on a strict least-privilege basis — captain sees what the captain needs, the chief engineer sees what the chief engineer needs, the chef does not see crew payroll.
This is exactly where a unified yacht management platform earns its keep. When charter bookings, crew records, maintenance logs, financial data and document repositories live in a single integrated system, the access model is built once, audited centrally, and revoked instantly when a crew member leaves. Compare this to the typical situation today: five different SaaS tools, five sets of credentials, five separate logout procedures when someone disembarks. Five chances to forget one.
"When operational data is consolidated on a single secure platform, the cybersecurity equation changes fundamentally. One identity model, one audit log, one DPA, one vendor to assess — instead of five."— Luca Longo, CEO SupaSailing
Crew Training: The Human Firewall
Technology alone does not stop social engineering. The single highest-leverage investment in yacht cybersecurity is consistent, plain-language crew training. The curriculum is not complicated:
- Recognise phishing — odd sender domains, urgent language, unexpected attachments.
- Verify out-of-band — if a port agent emails new bank details, confirm by phone using a known number.
- Lock devices when stepping away.
- Never plug in unknown USB drives.
- Report suspicious activity immediately to the captain or designated person.
Run a tabletop exercise once per season. Have one crew member play the role of "compromised laptop" and walk the team through the response: containment, communication, investigation, recovery. Doing this in calm conditions makes the real thing manageable. The SANS security awareness resources are an excellent starting point and translate well into a maritime context.
Incident Response When Something Goes Wrong
Assume that, despite every precaution, something will eventually slip through. The question is: how quickly will you contain it, and how confidently will you recover? A yacht-specific incident response plan should specify:
- Who to call: the management company's IT lead, the class society contact, the insurance hotline, the flag administration if required.
- Containment actions: which network ports to disable, which credentials to rotate, how to isolate the affected device without disrupting safety-critical OT.
- Evidence preservation: how to capture logs and disk images for forensic analysis without compromising chain of custody.
- Communication tree: who tells the owner, when, and how. What is shared with charter guests, what is not.
- Recovery: from which backups, in what order, with what verification.
Cyber Insurance: An Operational Reality
Cyber insurance for yachts has matured significantly in the last 24 months. Where five years ago coverage was either bundled into broader hull policies or unavailable, in 2026 most major maritime underwriters offer dedicated cyber products with clearly defined exclusions and conditions. The conditions are increasingly substantive: a baseline cyber assessment, evidence of MFA on critical accounts, documented backup procedures, and a written incident response plan are now common minimum requirements.
The underwriting conversation is also a useful diagnostic. The questions an insurer asks during a cyber proposal — about network architecture, vendor management, third-party access, log retention, training cadence — map closely to the controls that genuinely reduce risk. Many operators report that the proposal process itself, even before coverage is bound, surfaces gaps that would otherwise have remained invisible until the next incident.
Vendor and Sub-Processor Risk
Most yachts in 2026 depend on a chain of vendors and sub-processors: the management company's accounting platform, the charter booking system, the maintenance app, the satellite communications provider, the entertainment system, the crew payroll service. Each of these has access to some slice of the operation's data. Each represents a potential entry point.
The discipline of vendor risk management — once a corporate IT concern — is now a yacht IT concern. Maintain a written vendor list. Sign Data Processing Agreements with every vendor that handles personal data. Verify that significant vendors carry meaningful certifications such as SOC 2 Type 2 or ISO 27001. Know which sub-processors your primary vendors use, and where their data is hosted geographically.
SupaSailing's Approach
At SupaSailing we treat security as a precondition, not a feature. Our fleet management platform, charter operations, marina software, brokerage CRM and refit project management all run on the same hardened foundation: AES-256 encryption at rest, TLS 1.2+ in transit, application-level encryption for sensitive tokens, AWS KMS-managed keys with rotation, full audit logs, role-based access control with MFA, SAML SSO for enterprise teams, and EU data residency.
This matters because — as we explained in our recent article on AI in yachting — when operational data is consolidated on a single secure platform, the cybersecurity equation changes fundamentally. One identity model, one audit log, one DPA, one vendor to assess — instead of five. Read our full security and compliance posture here.
Where to Start
If you are reading this and your yacht has never had a formal cyber assessment, you are not alone. Most operators are in the same situation. The ten-day plan looks like this:
Days 1–2: Inventory every connected device, every account, every shoreside integration.
Days 3–4: Audit your network: is OT segregated? Is the firewall actively maintained?
Days 5–6: Roll out a password manager and enforce MFA on every business-critical account.
Days 7–8: Run a phishing-awareness session with the entire crew.
Days 9–10: Document the incident response plan and store a printed copy somewhere accessible.
Done in this order, the work is achievable in a single off-season call. And the payoff — the dramatic reduction in attack surface, the alignment with MSC.428(98), and the simple peace of mind — is, frankly, the best return on investment in maritime IT today.
To learn how SupaSailing's integrated platform supports yacht cybersecurity from the ground up, get in touch or request a demo.
Satellite and Onboard Connectivity Risks
The shift to high-bandwidth satellite connectivity — Starlink, OneWeb, OmniAccess — has fundamentally changed the cyber risk profile of yachts. Where five years ago a vessel might have been online intermittently and at low bandwidth, in 2026 a typical superyacht maintains continuous gigabit connectivity. The benefits for guests, crew operations and predictive maintenance are real. The exposure is also real.
The most significant change is that the yacht is now continuously addressable from the open internet. Any vulnerability in any onboard system that has accidental WAN exposure becomes exploitable in real time. Configuration discipline that was acceptable in an "occasional connectivity" world is no longer acceptable. The remedy is not to retreat from connectivity — that ship has sailed — but to take connectivity as seriously as any commercial enterprise: managed firewalls, intrusion detection, regular external penetration tests, and a clear rule that no system on the yacht has an externally reachable management interface unless explicitly required.
The ENISA maritime threat landscape report updates annually and is one of the better authoritative resources for understanding the evolving threat picture.
The Crew-Owned Device Problem
One of the most under-discussed cybersecurity issues on yachts is crew personal devices. Crew members live aboard, often for months at a time, and use the onboard Wi-Fi for personal communications, banking, social media, streaming, and increasingly cryptocurrency transactions. These devices are typically not centrally managed, not patched on a corporate cadence, and not subject to any kind of endpoint protection regime. They are also, often, on the same network segment as operational systems.
The architecturally clean answer — strict crew-network isolation, mandatory device enrollment in a mobile device management programme, no exceptions — is operationally expensive and culturally unpopular. The pragmatic compromise that works for most yachts: a fully isolated crew personal Wi-Fi network with no path to operational systems; a separate crew operational network for work devices that the management company controls; and clear written policies on which network to use for what. The discipline of network labelling — visible on the SSID and reinforced in onboarding — pays off the first time a crew member's compromised personal laptop fails to reach the bridge electronics.
Frequently Asked Questions
Does IMO MSC.428(98) apply to private yachts?
Strictly speaking, MSC.428(98) applies to vessels covered by the ISM Code, which is mainly cargo and passenger ships above 500 GT. Private yachts below that threshold are not formally in scope. However, port-state control inspections and class society notations increasingly examine cyber readiness on yachts of all sizes operating commercially under charter. Treating it as the practical baseline is the prudent default in 2026.
What is the realistic budget for a basic cyber programme on a 50-metre yacht?
For a yacht of this size, a competent first-pass cyber programme — initial assessment, network segmentation, password manager rollout, MFA enforcement, basic crew training, and a documented IR plan — typically costs in the range of €15,000 to €40,000 in year one, with annual maintenance of €5,000 to €15,000 thereafter. This is a small fraction of the cost of any single cyber incident.
How often should we run a tabletop exercise?
Once per off-season is the practical minimum. The exercise itself takes 90 minutes, costs nothing beyond crew time, and dramatically improves the response when an actual incident occurs. The crews that run tabletop drills find that their first real incident feels like the third or fourth, not the first.
Is Starlink a security risk?
Starlink itself is a competent satellite internet service. The security risk is not Starlink — it is the assumption that "having internet" is a binary state rather than an architectural choice. The yacht with continuous connectivity needs continuous security discipline. The yacht that bolts Starlink onto an existing flat network without rethinking segmentation has substantially increased its attack surface without acknowledging it.
Should we hire an external cyber consultant?
For most yachts, yes. The breadth of expertise required — network architecture, OT security, regulatory compliance, incident response, training delivery — is unrealistic to maintain in-house on a single vessel. The competent external consultant brings cross-fleet experience and pattern recognition that the in-house team simply cannot. Choose a consultant with a documented maritime track record, not a generic IT security firm.
Related solutions
See how SupaSailing is built around these roles:
See SupaSailing in action
Book a free demo call and discover how one platform can run your charter, marina, fleet, shipyard or brokerage.
Book a Free DemoShare this article